

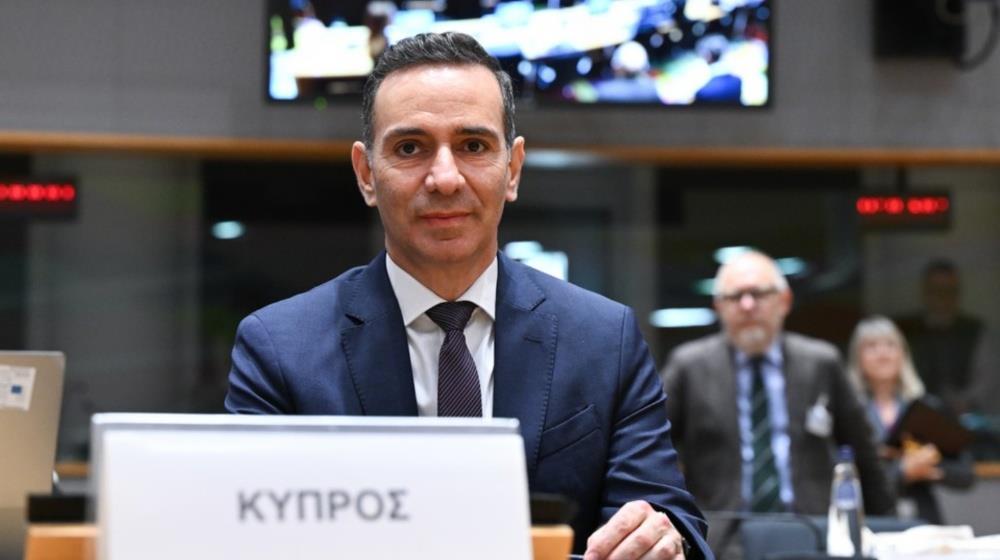
The task at hand is to build products people can trust with regard to the cybersecurity perspective, Deputy Minister of Research, Innovation and Digital Policy, Nicodemos Damianou, said on Monday, addressing a conference in Nicosia entitled "Building CRA compliance through horizontal cybersecurity standards".
Referring to the Cyber Resilience Act (CRA), Damianou said that on 11 September the first obligations deriving from the Act came into force, adding that manufacturers must now report actively exploited vulnerabilities and severe incidents through the European Union Agency for Cybersecurity (ENISA) reporting arrangements under the Act. He also noted that the full set of essential requirements will apply to every product that includes digital elements on the European market.
Under the Commission's standardisation request, the European Committee for Standardisation (CEN), the European Committee for Electrotechnical Standardisation (CENELEC) and the European Telecommunications Standards Institute (ETSI) are developing harmonised standards that will support implementation of the CRA, such as secure design, vulnerability handling, the requirements that apply to every product irrespective of what that is, Damianou said. "These standards give manufacturers something enormously valuable: One clear, recognised route to compliance, instead of twenty-seven interpretations of the same article," he emphasised.
"Cyprus held the Presidency of the Council of the European Union until June. Before it began, I told my fellow ministers in Brussels that cyber resilience would be one of our three digital priorities — because sovereignty and autonomy are not about isolation,’’ the Deputy Minister noted.
"We proceeded with the revision of the Cybersecurity Act — a stronger ENISA, simpler certification — and brought it before the Telecom Council in June. We welcomed Europe's cybersecurity certification community here in Cyprus,’’ he pointed out, adding that "the Digital Omnibus, with its promise of a single entry point for incident reporting, is now in the hands of the Irish Presidency.’"
Damianou also stated that "Europe cannot afford to be merely a regulator of technologies developed elsewhere.’’
Referring to the actions taken by Cyprus, Nicodemos Damianou said that "the Digital Security Authority is at the centre of our preparations for the CRA.’’ He further added that this summer, the Council of Ministers approved, for the first time, a unified, complete and encompassing Cybersecurity Policy Framework for the government and the broader public sector.
Referring to Cypriot small and medium-sized enterprises (SMEs), the Deputy Minister pointed out that "most Cypriot manufacturers and software developers do not have a compliance department.’’
"For them, a practical, accessible standard is the difference between compliance as a burden and compliance as a competitive advantage,’’ he noted.
He went on to say that ‘’the CRA is not only a cybersecurity measure. It is also a Single Market measure.’’ ‘’A company that builds secure products once should be able to place them confidently across the European market,’’ he emphasised.
"The huge task at hand is at the end of the day to build products people can trust from a cybersecurity perspective,’’ he concluded.