

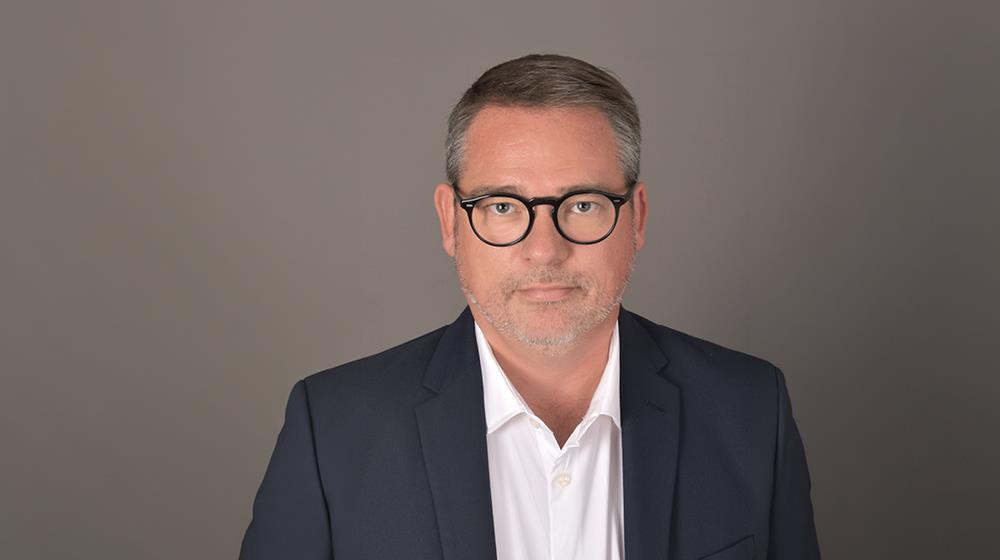
Rogier Soer is Head of Cyber EMEA at AIG, leading the company's cyber insurance strategy and underwriting activities across Europe, the Middle East and Africa.
With more than 20 years of international experience in cyber insurance and financial lines, he has held senior leadership roles at AIG and AXA, where he helped pioneer cyber insurance solutions in Europe. He is a recognised expert in cyber risk, cyber resilience and emerging technology threats, regularly advising clients and brokers on managing evolving cyber exposures.
Cyber threats continue to evolve at an unprecedented pace. How has the cyber risk landscape changed over the past few years, and what concerns business leaders the most today?
The pace of change in recent years outstrips anything we have seen in the years since AIG launched one of the industry's first cyber insurance programmes. Three shifts stand out. First, cyber has become a supply chain risk: many serious incidents start with a third party – a software vendor, a cloud provider, etc. – which can create significant exposures for the client. For example, a single security vulnerability in one supplier's software can expose data for hundreds of thousands of individuals at once. Second, threat actors have become more sophisticated, and ransomware remains their tool of choice. What starts with a simple phishing e-mail can quickly escalate into system-wide encryption, data theft, and extortion, sometimes with stolen data offered for sale on the dark web. Third, AI is reshaping both sides: criminals can use AI tools to create highly credible deepfakes even as defenders leverage AI’s capabilities to sharpen their threat intelligence. Regardless of the form the threat takes, what should concern business leaders the most today is not the breach itself, but the business interruption, dependency on suppliers they do not control, regulatory obligations across multiple jurisdictions, and the reputational impact on relationships with customers and partners.
Many organisations still view cyber insurance as something they only need after an incident occurs. Has the role of cyber insurance changed?
Cyber insurance today should be a partnership across the entire lifecycle of the risk, not a product you take out of the drawer after a loss. Our approach at AIG goes well beyond insuring against cyber threats – we actively work with our clients to prevent them through complimentary loss control tools like employee training and phishing simulations, vulnerability scanning, darknet credential monitoring, ransomware risk assessments, tailored incident response plans, and more. We also have an in-house team of cyber risk experts drawing on insights from more than 10,000 cyber claims to help our clients manage their cyber risk. This support and analysis deliver tangible results: we have alerted over 400 clients mid-policy to unpatched vulnerabilities and malware findings before they became incidents, and for clients using our Blacklist IP Blocking service, around five million connections are blocked every month. The real value of an effective cyber policy shows itself long before an incident ever takes place.
Organisations often underestimate the complexity of recovering from a cyberattack. Beyond financial compensation, what kind of support do clients really need?
A serious cyber event is never just an IT problem. What clients need in those first hours after an attack is not a cheque; it is the experience and expertise to coordinate the immediate response: a forensic investigation, procedures for notifying regulators and affected individuals, customer communication, media scrutiny, potential extortion negotiations, and the operational pressure of quickly restoring systems. Few organisations have all those specialist capabilities on standby. That is why our emergency incident service ‘First Response’ is included with primary cyber policies, providing our clients with access to a 24/7 hotline, a Legal Response Advisor in contact within one hour, an IT specialist to help our clients contain the issue and restore their systems, initial guidance on notification requirements, and, where needed, a crisis communicator and cyber extortion advisor. With ‘First Response’, we have supported a client hit by a ransomware attack to restore critical systems quickly, meet their regulatory obligations, and avoid paying a ransom. In another case, our client obtained an injunction to stop their stolen data advertised on the dark web from being used or disseminated. In the event of a cyber incident, speed, specialist expertise and coordination are what turn a potential catastrophe into a managed event.
Many businesses today operate internationally. How important is it for cyber insurance programmes to have multinational capabilities?
As businesses expand into new geographies, it is increasingly critical they consider their cyber insurance needs across jurisdictions. If a group's subsidiaries are recognised as independent data controllers or processors under local law, regulatory investigations could be brought locally – and a local policy may be required to achieve local payment. Each subsidiary may also depend on an entirely different supply chain, and local subsidiaries may have contractual requirements from their own customers to evidence locally compliant cyber cover. This is where AIG's multinational capability is a key differentiator: we can deliver solutions in more than 200 countries and jurisdictions, supported by over 500 dedicated multinational service professionals, with capabilities ranging from traditional cover to highly specialised offerings.
If you could leave business leaders with one key message about cyber resilience, what would it be?
Cyber resilience is built before an event occurs, not bought after it. Organisations should treat cyber as an enterprise risk, not an IT risk. That means understanding your third-party dependencies, knowing how AI is being used inside and around your organisation, and putting governance in place early. And remember that AI, like every new technology, is a two-way street – it can heighten exposure, but it can also help you identify weaknesses and respond faster. The organisations that come through incidents well are those that prepared and engaged their insurer as a partner long before anything went wrong. When prevention, rapid response and risk transfer work together, a cyberattack becomes a manageable event, not an existential threat.