

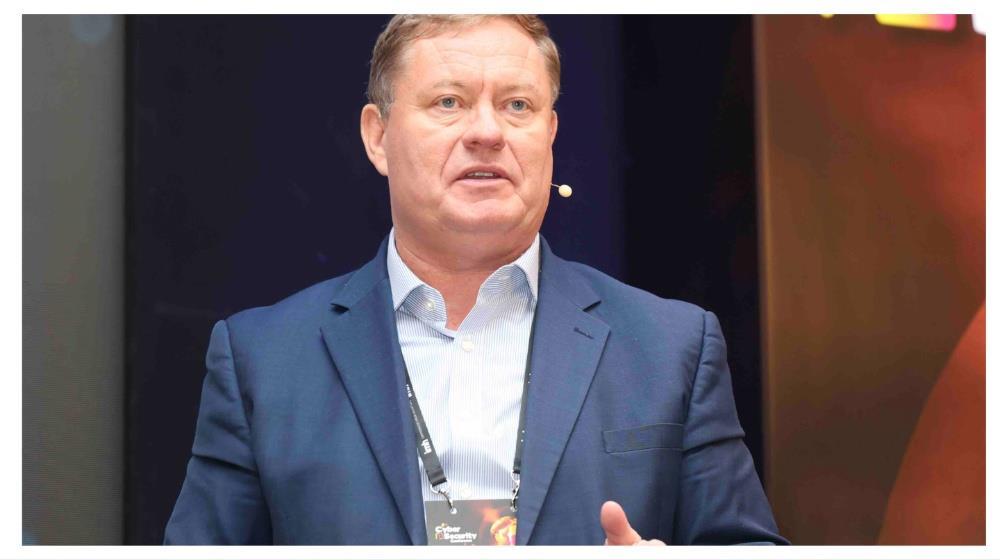
The changes brought about by advanced artificial intelligence and open-source models to the cyber risk landscape were analysed by Cónal Hickey, Vice President, Security & Resiliency Practice Leader SM, Kyndryl, in his presentation entitled 'The New Cyber Risk Landscape: Security and Resilience in the Frontier AI Era' at the 6th Cyber Security Conference.
Hickey cited new data emerging five months after the Mythos model was released, looking at how new AI models are impacting the risk profile of businesses. The data shows that the volume of published vulnerabilities in the second quarter of 2026 jumped 2.7 times compared to the same period in 2025. Most worryingly, 61% of the vulnerabilities that were attacked were initially rated below the critical risk level, meaning that traditional audits that focus only on very serious security gaps are leaving businesses exposed.
Artificial intelligence is dramatically speeding up malware development, as in a controlled study it took less than an hour to create the first working browser exploit.
He made particular reference to the steps organisations need to take to prepare for new threats, emphasising that success is now measured by how quickly exposure to risk is reduced and not by how quickly patches are implemented.
Security leaders must broaden their intelligence sources, prioritise risks based on the actual accessibility of their systems, and bridge the remediation gap by applying artificial intelligence to validate findings. In addition, he noted that banks supervised by the European Central Bank are required to submit a comprehensive action plan by 31 October, which must cover attack surface visibility, vulnerability response speed, continuous monitoring, supply chain governance, defense in depth, and data recovery readiness.
Finally, he focused on the need to move from periodic measures to a continuous business risk management process, leveraging Kyndryl’s experience from critical infrastructure and organisations across industries. Internal data from the Kyndryl Bridge platform reveals that the European Central Bank’s systemic banks lag behind the global average, with an average of 42% of their devices without the necessary security updates and recording 107 serious exposures per device, while leading organizations limit these rates to 1%.
(Source: InBusinessNews)