

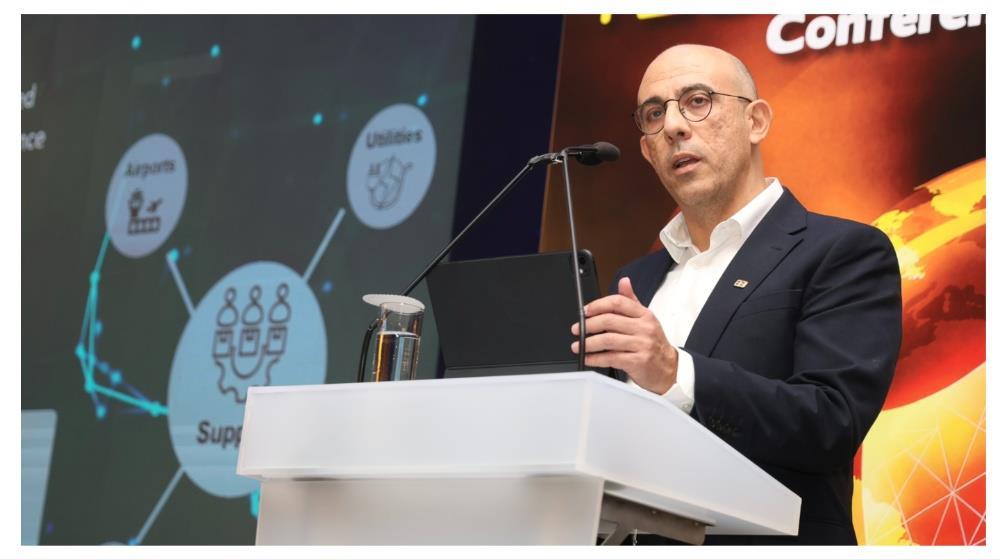
The evolution of the digital security landscape beyond the narrow boundaries of compliance was analysed by Marios Pieris, Commissioner for Communications, in the context of his presentation entitled 'Beyond Compliance' at the 6th Cyber Security Conference.
Pieris put particular emphasis on the Republic of Cyprus' strict decision to set the time frame for submitting the first warning at just six hours from the moment an organisation becomes aware of a significant incident. This regulation, which was established based on the Central Administrative Act 281/2026, is clearly stricter than the general European framework of NIS2 which provides for 24 hours.
As the Commissioner explained, such a record speed in reporting can only be achieved through structures that have been built and tested in practice long before the crisis hit. Digital crime now operates as a fully professional industry, while the interconnection of services causes chain reactions that turn a local problem into a national one.
Indicatively, the European Union Agency for Cybersecurity (ENISA) analysed approximately 4,900 serious European incidents, with public administration, critical infrastructure, hospitals and airports being the main targets.
At the same time, he presented the results of the national audits, revealing that almost half of the required security mechanisms have not yet been implemented. The average digital maturity of the audited Cypriot organisations is only 1.6 with an excellent score of 3, which shows that the common security base is implemented in a very uneven manner.
The data shows that 49% of necessary controls remain at a very early or fragmented stage, with one-fifth of organisations falling below the baseline of 1.0. The most troubling finding is that the weaknesses are not in technology, but in governance, risk management, and identity and access management, which is the number one national security gap.
It is noteworthy that, according to the Commissioner, only during the period June - August 2026, the national CSIRT team managed 544 malicious email addresses and recorded attacks in critical sectors such as energy, health, telecommunications and public administration.
In his presentation, Pieris emphasised that the NIS2 directive is not the final destination, but the catalyst for changing the way digital risk is managed. Compliance is simply the starting point, but resilience is what demonstrates whether an organization can prevent, withstand and recover from an attack.
This responsibility lies exclusively with top management, which by law must approve the measures, supervise them and be appropriately trained, as security can no longer be assigned exclusively to IT departments. To strengthen market skills, the Office of the Communications Commissioner invests directly through the ICT Academy, which has organized 285 events with the participation of 9,054 professionals.
Pieri concluded that the goal of businesses should not be to show documents during an audit, but to demonstrate their true resilience when tested.
(Source: InBusinessNews)